Demo
Building a Repeatable and Hardened Vault POC
You don't need to spend a lot of time and energy to give your HashiCorp Vault deployment production hardening.
Do you use the root token for everything? Are your Vault policies wide open? Did you ignore setting up TLS? While there is nothing wrong with taking some shortcuts in building out a Vault proof-of-concept, have you ever had a POC that "magically" started being used as production?
What You'll Learn
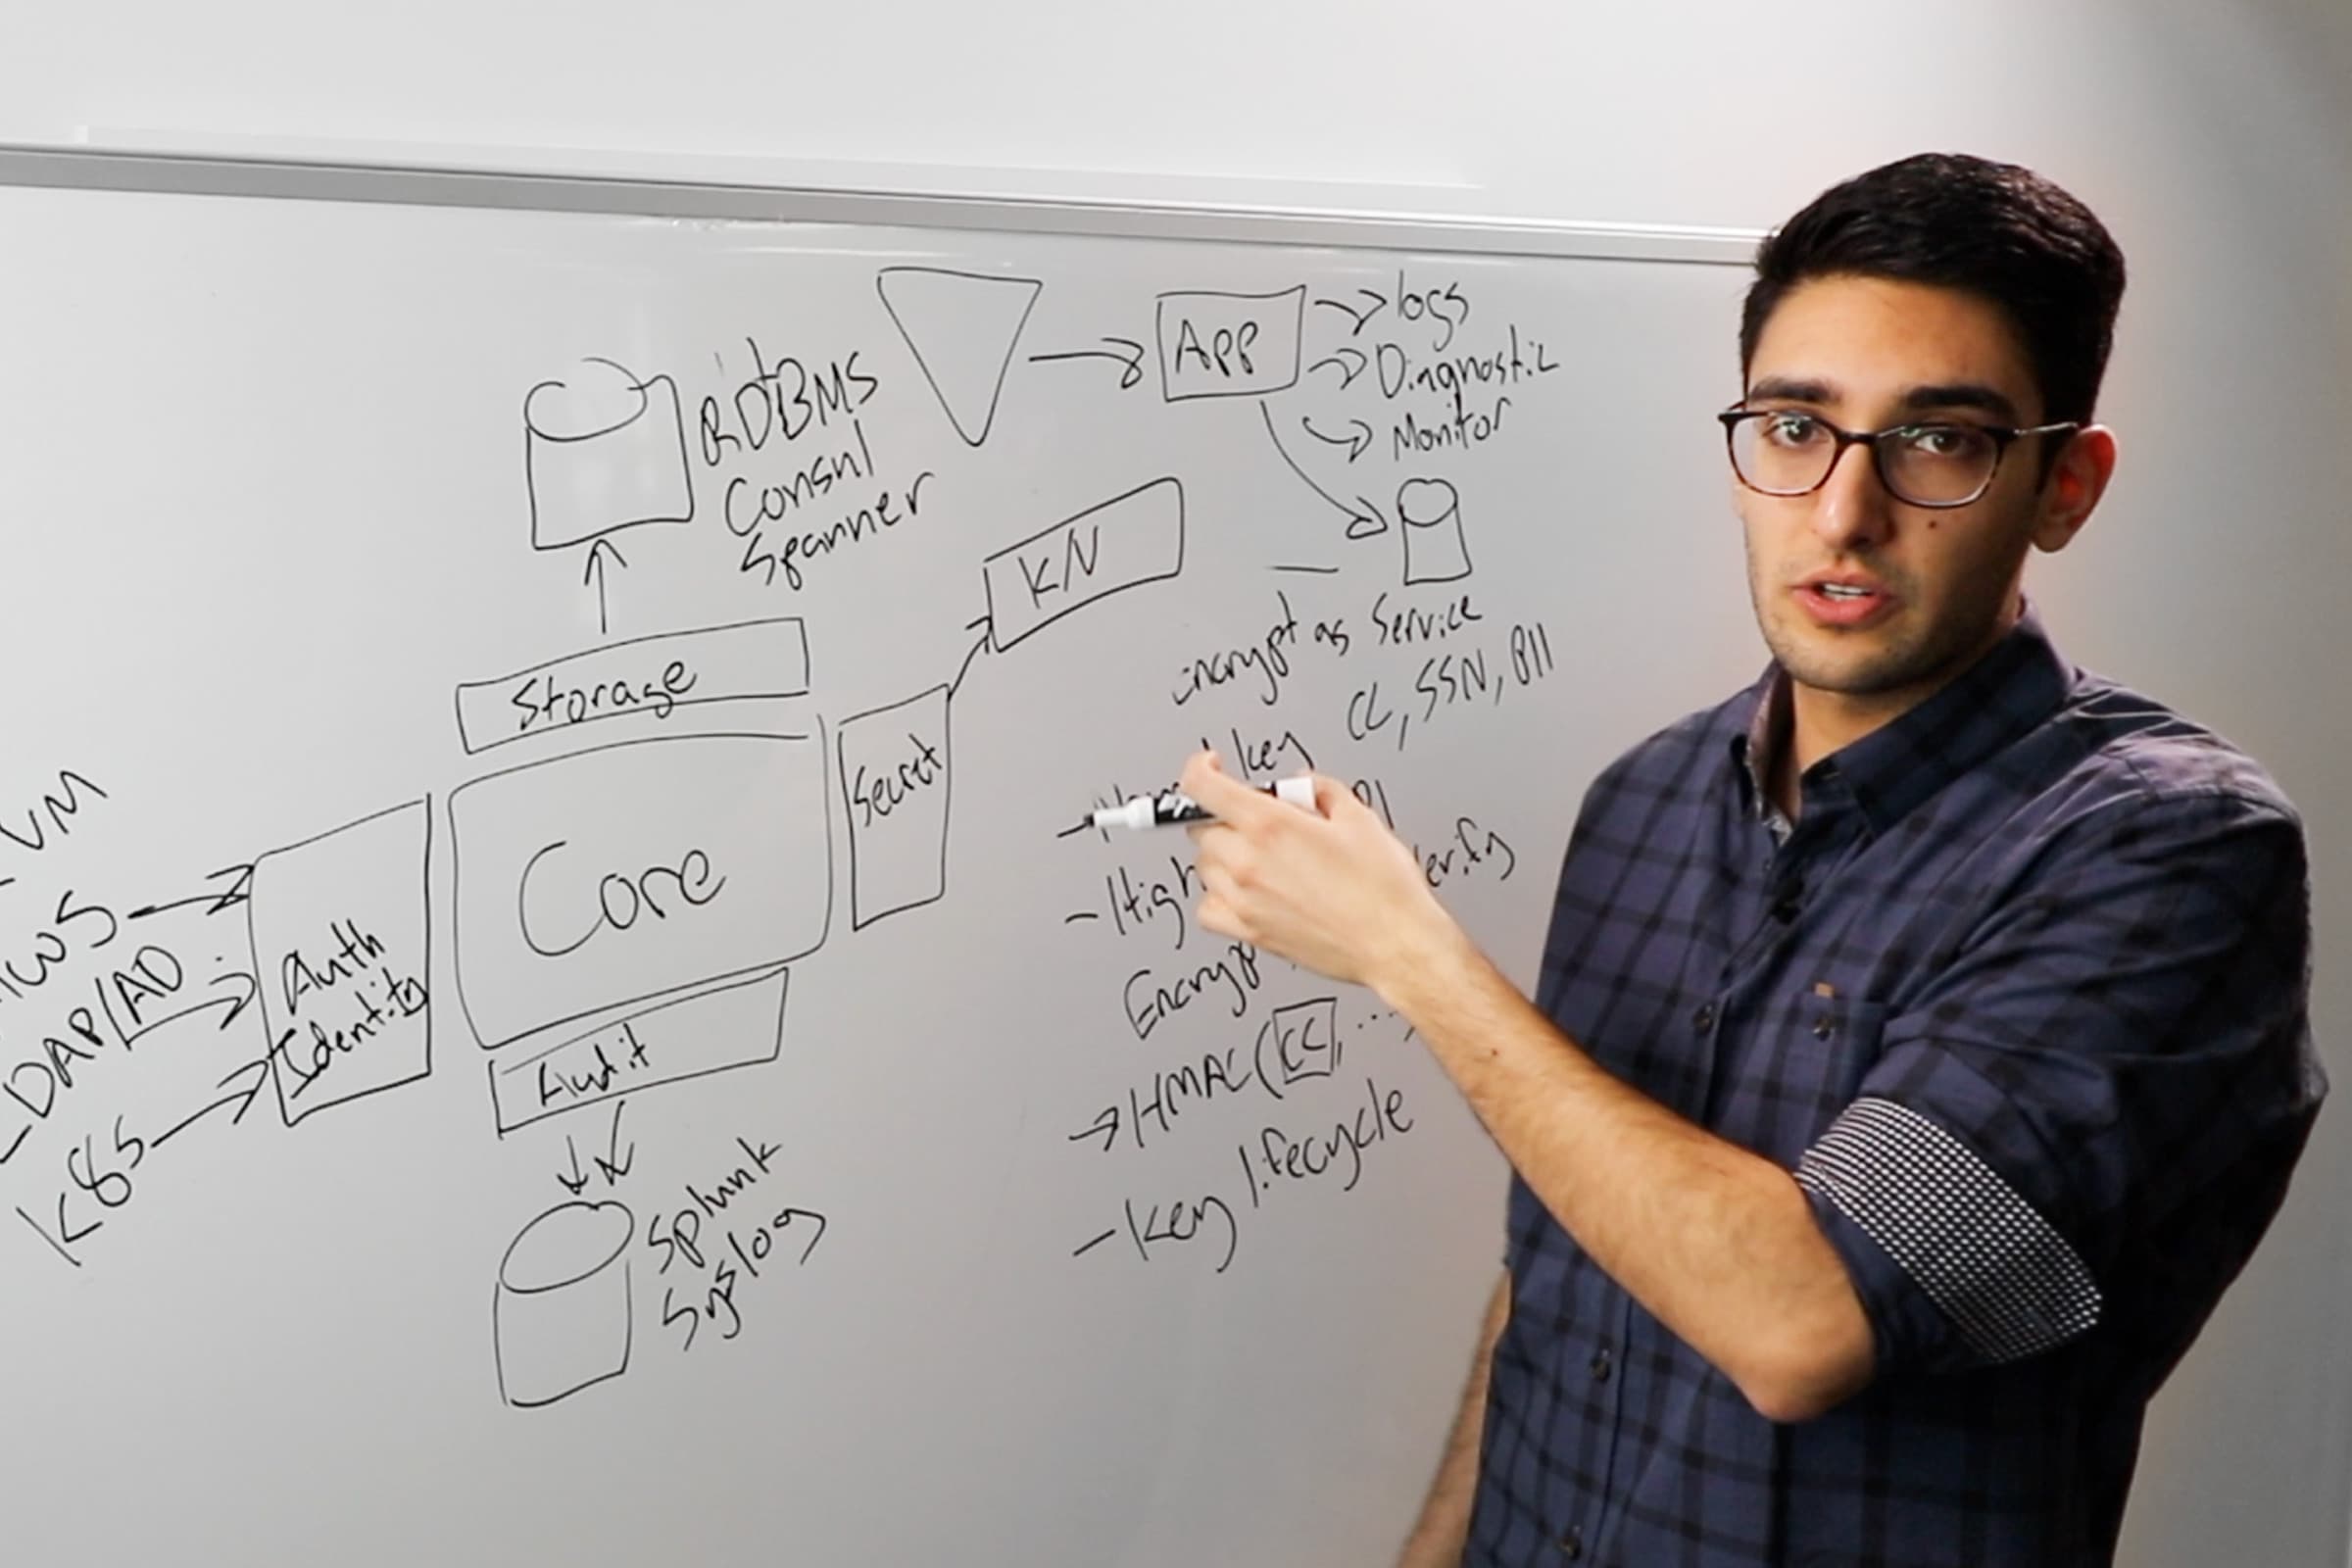
In this talk Gabe Maentz showcases a few simple steps that you can take to apply Vault's hardening best practices without requiring a lot of time and energy.